Physical Key Return Policy and Offboarding Best Practices


Published: Aug 21, 2026

Note: If you are looking to uninstall a Microsoft Office product key via Command Prompt, this is not that software guide. This article is an operational blueprint designed for facilities managers, HR professionals, and IT administrators looking to secure physical corporate offices, keys, RFID key fobs, and biometric systems during employee offboarding.

When an employee departs an organization, IT departments typically execute a structured digital de-provisioning process: they revoke Slack access, deactivate Google Workspace accounts, and suspend Salesforce permissions. However, a significant gap frequently remains at the physical doorway.

According to industry security studies, up to 48% of terminated employees retain physical or digital access to company facilities after their official departure. This oversight is a major liability; corporate risk data reveals that 56% of companies identify former employees as their leading source of insider threat risk. Developing a secure, standardized physical credential offboarding policy is essential to protecting your physical assets and intellectual property.
Why Getting the Physical Key Fob Back is a False Security Blanket


Many operations managers believe that reclaiming a physical credential means a facility is secure. This is a dangerous security illusion.

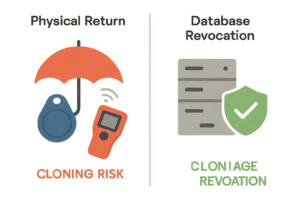
This visual clarifies that merely returning a physical key fob does not eliminate security risks because cloning can bypass physical possession. Immediate database-level deactivation within your access control system is essential for security.

Older RFID proximity cards operating on legacy 125 kHz frequencies can be easily cloned in less than ten seconds using inexpensive devices purchased online. An employee can hand back their physical card while retaining a perfectly functional duplicate.

Therefore, retrieving the hardware is merely a cost-saving measure for inventory recycling. True security is achieved only through immediate, database-level revocation within your physical access control system.

If your facility relies on traditional lock-and-key setups, a lost or unreturned key might necessitate commercial rekeying or a complete commercial door lock replacement to re-establish a secure perimeter.


Managing Biometric Data Removal Post-Employment


The shift toward biometric authentication—using fingerprints, facial geometry, or iris scans—offers streamlined access, but introduces substantial legal liabilities. Under frameworks like the Illinois Biometric Information Privacy Act (BIPA) and the EU’s GDPR, organizations face severe statutory damages of $1,000 to $5,000 per individual violation for failing to adhere to strict consent, retention, and permanent destruction schedules.

Leaving a terminated employee’s biometric data on localized door readers or central databases post-employment is a major class-action lawsuit trigger.

To mitigate regulatory risk, your HR-security checklist must include these biometric de-provisioning protocols:

  1. Revoke Access Rights: Instantly disable the user’s authorization profile within the access control software.
  2. Purge Edge Readers: Ensure that biometric templates stored locally on edge door readers are completely overwritten.
  3. Wipe Central Backups: Permanently delete localized server backups containing biometric data signatures.
  4. Issue Destruction Receipts: Provide a formal “Biometric Data Destruction Certificate” to the departing employee as written proof of compliance.

Automating Physical Access Deactivation: From HRIS to Lock


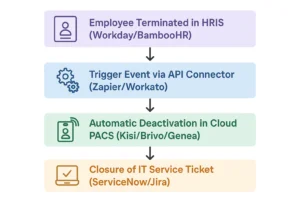
This flowchart educates readers how modern physical access systems can be seamlessly integrated with HR platforms via API automation to ensure immediate and error-free access revocation upon employee offboarding.

Manual offboarding processes are highly prone to human error. If an HR administrator forgets to email the facilities manager about an employee’s termination, that departed individual may retain access to the building indefinitely.

To solve this, modern enterprises connect their Human Resources Information System (HRIS) directly to their Physical Access Control System (PACS). Leveraging advanced API integrations alongside keyless entry systems for small business removes manual delays from the security workflow.

This integrated approach guarantees that physical access is terminated the exact second an employee is marked inactive in HR records, providing a reliable, automated safety net.


Frequently Asked Questions


What should we do immediately if a departing employee loses an office key?

If an employee loses a mechanical key, assess the security risks of your specific lock system. For a comprehensive breakdown of the decision-making process, read our expert guide: should i change my locks if i lose my keys.

Can cloud-based keyless entry systems be bypassed or hacked?

While no network is 100% impenetrable, modern enterprise PACS systems use high-grade end-to-end encryption that is vastly more secure than traditional lock systems. Learn more about system vulnerabilities in our detailed analysis: keyless door entry system security.

How can our business upgrade from physical keys to automated electronic access?

Partnering with a professional commercial locksmith allows you to audit your entry points, select the right hardware, and integrate your systems with your IT directory. If you are ready to modernize your building’s security framework, contact our professional commercial locksmith service to schedule a consultation.

Model Employee Key Fob & Office Key Policy Template


Implementing a transparent, legally binding policy ensures that employees understand their responsibilities regarding physical credentials. Organizations can copy and adapt this standardized template:

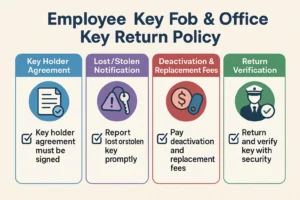
This memory aid reinforces the critical components of effective physical access credential policies, making it easy to remember and implement structured offboarding procedures.

Corporate Physical Access & Key Return Policy

  1. Access Credential Responsibility: All issued physical credentials (brass keys, RFID fobs, mobile credentials) are the property of the organization. Under no circumstances may credentials be shared, transferred, or duplicated.
  2. Loss Reporting Requirement: Employees must report lost or stolen access credentials to Security within 2 hours of discovery.
  3. Mandatory Return Protocol: Upon notification of termination or resignation, employees must surrender all physical keys and fobs to Human Resources during their exit interview.
  4. Immediate Database Revocation: Independent of physical return, all electronic credentials will be systematically disabled within 1 hour of the employee’s official departure time.
  5. Key Replacement Liabilities: Unreturned master keys can compromise the building’s physical security. If a critical master key is lost, the cost of rekeying the facility may be charged to the departing department’s operating budget.


Replacing legacy master keys is a costly endeavor. Re-keying a commercial facility can range from $2,000 to $50,000 depending on size and complexity. By contrast, a professional Electronic Access Control (EAC) installation averages $3,500 per door, paying for itself over time by eliminating the need for physical rekeying during typical employee turnover cycles.


Multi-Site Retail Key Management

For high-turnover operations, managing physical credentials poses a unique operational challenge. If a departing manager leaves with a physical master key, the entire retail location is vulnerable.

To mitigate this risk, multi-site businesses rely on smart key cabinets that track the real-time location of keys and mandate automated handovers. Utilizing high security commercial locks with restricted, patented keyways prevents unauthorized duplication, ensuring departed employees cannot retain copies of active physical keys.


Need more information? Get a free quote

Call us now

Get A Free Call From Our Experts!

Floating Button Form