Cloud-Based Access Control for Multi-Location Businesses | SLK


Published: Sep 30, 2026

Managing a multi-site physical security infrastructure is fundamentally an architectural challenge. For IT Directors and Security Chiefs, the friction isn’t about understanding the cloud—it is about managing transition risks. How do you centralize global governance while delegating local operational control? How do you scale without massive “rip-and-replace” expenditures, and how do you protect your corporate network from IoT-focused physical security exploits?

Deploying modern types of access control systems across distributed architectures requires an approach that balances physical wiring realities with cloud-native capabilities.

The Multi-Site Access Dilemma: Central Governance vs. Local Autonomy


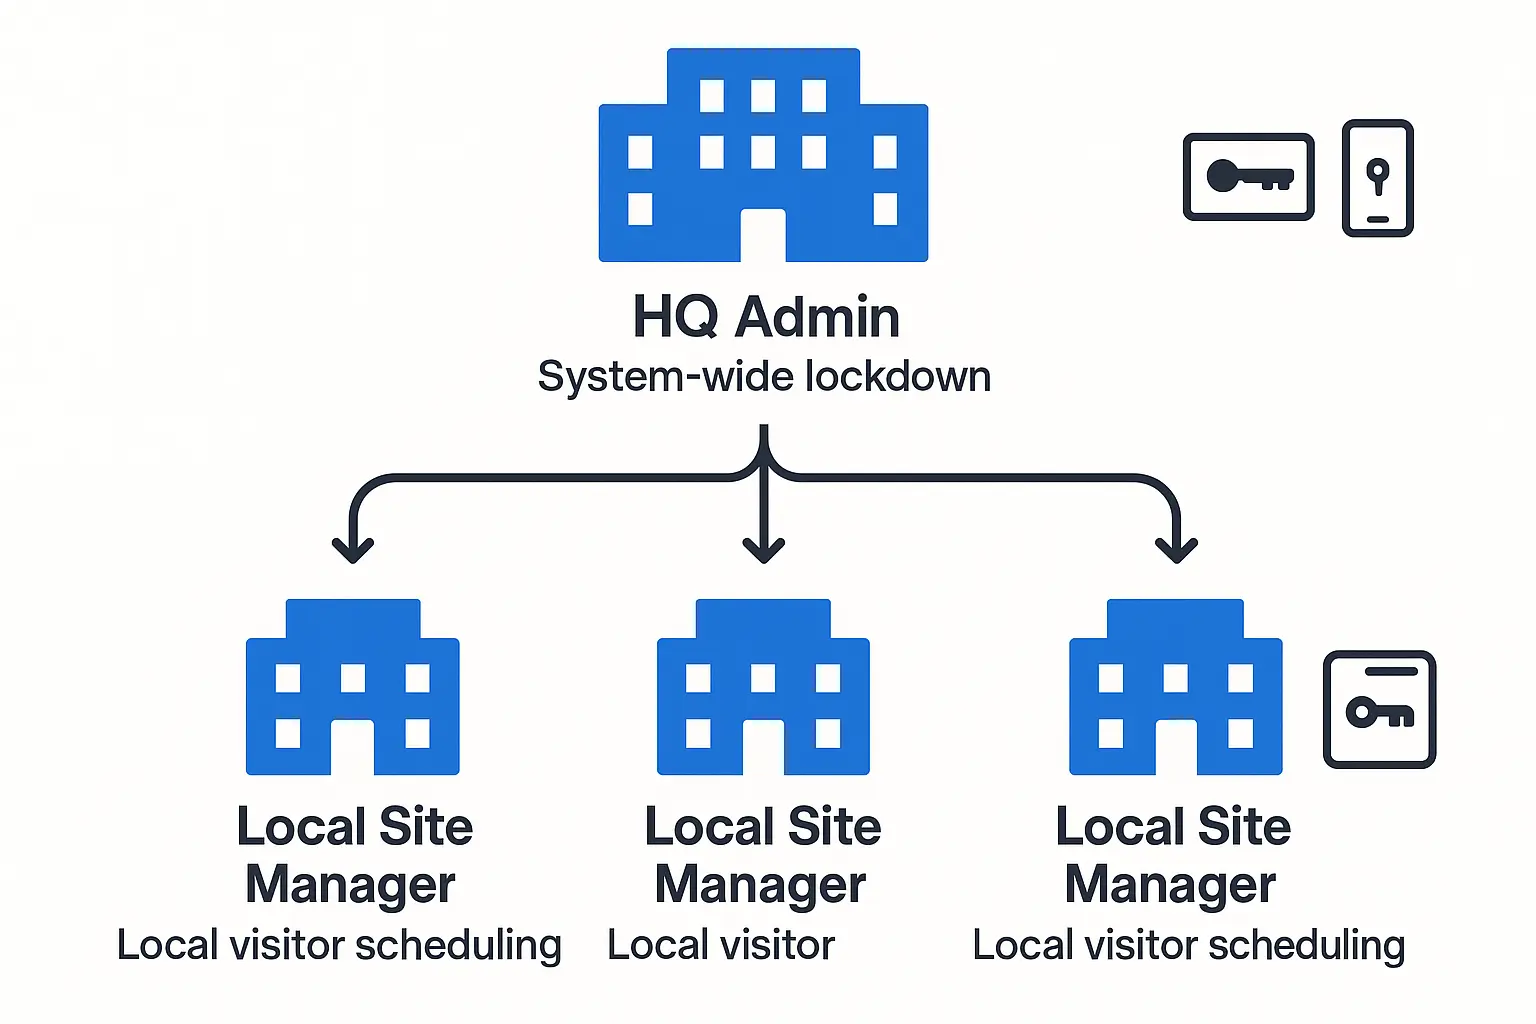
This image illustrates how cloud-based access control balances centralized system-wide governance with delegated local site management through role-based administration, clarifying core operational control concepts for multi-location businesses.

In multi-location operations, a rigid security policy fails. Enterprise environments require a “delegated administration” model. Under this architecture, the corporate IT headquarters establishes global security baselines, manages system-wide directories (e.g., Okta, Azure AD), and retains emergency global lockdown capabilities.

Concurrently, local site managers require the autonomy to adjust localized access schedules, issue temporary digital credentials, and review local entry logs. Cloud-based systems handle this via granular Role-Based Access Control (RBAC). Security profiles are tied to directory attributes, ensuring that when an employee’s role changes in your Identity Provider (IdP), their physical access permissions across all geographic branches update in real time without manual administrative intervention.

The Mechanics of Offline Failover (What Actually Happens During an Outage?)


This flowchart breaks down the offline failover process in cloud access control, showing how offline caches in readers and controllers enable continuous door access and automatic secure synchronization once connectivity is restored.

The single greatest point of evaluation anxiety for cloud deployments is a network outage. If the local internet connection drops, doors must remain operational.

Reliable cloud architectures solve this through local edge-intelligence. Instead of depending on real-time cloud authorization for every badge-swipe, physical access control units utilize a dual-layer offline caching mechanism:

  • Reader-Stored Cache: Modern smart readers temporarily store credential hashes for high-frequency users to ensure rapid, sub-second door unlock times.
  • Controller-Stored Cache: The physical control panel at the edge functions as a localized server database. These controllers routinely cache up to 100,000 active user profiles and store up to 50,000 historical event logs locally.

When an ISP outage occurs, the edge controller continues evaluating, authorizing, and logging every entry attempt. Once the internet connection is restored, the controller automatically establishes a secure WebSocket or HTTPS connection to synchronize its offline log queue back to the cloud database.

Retrofitting Legacy Systems: The 3-Step Migration Blueprint


Total system replacement is rarely financially or operationally viable. Most multi-site organizations manage a mix of modern facilities and legacy properties equipped with standard types of commercial door locks. Transitioning to the cloud without a complete tear-out requires a phased, three-step blueprint.

Physical Protocol Upgrades

Evaluate your existing reader wiring. Over 70% of legacy installations rely on the Wiegand protocol, which transmits unencrypted data, exposing systems to credential skimming with cheap pocket tools [^3]. Upgrading to the Open Supervised Device Protocol (OSDP v2) is mandatory. OSDP standardizes AES-128 bidirectional encryption between the reader and the controller, eliminating physical-layer vulnerabilities.

Controller Retrofitting

You do not need to replace your entire physical infrastructure. In many deployments, you can preserve legacy steel enclosures, power supplies, and cabling, and simply swap the proprietary legacy control boards with modern open-hardware or cloud-native controllers. This minimizes hardware capital expenditure while instantly modernizing your software footprint.

Hybrid Credential Rollout

With over 65% of enterprises transitioning to mobile credentials (NFC/BLE) over the next two years [^2], managing a phased transition is critical. Multi-technology readers allow you to support legacy physical proximity cards alongside modern mobile apps. This ensures seamless employee transit during the phased rollout, allowing you to retire physical credentials on your own timeline. Integrating a secure key fob door entry system alongside mobile apps provides a robust fallback configuration.
Frequently Asked Questions


What happens to my physical doors if the cloud software experiences a central service outage?

If the central cloud service platform goes offline, your doors continue to operate normally. The local edge controllers handle all access authorization and log caching using their internal databases. Employees will experience no disruption when presenting authorized credentials; data will resynchronize automatically once cloud service is restored.

Can I run a cloud access control platform using my existing wiring and readers?

Yes, in many cases. Many cloud-native platforms can utilize your existing low-voltage reader cabling and power supplies. However, to ensure modern security standards, legacy unencrypted Wiegand readers should be upgraded to OSDP-compatible readers to protect against badge cloning.

How does cloud access control lower the Total Cost of Ownership (TCO)?

Cloud-based systems eliminate the substantial CapEx and ongoing OpEx associated with dedicated on-premises security servers, Windows Server licensing, database management, and manual software patching. Instead, software maintenance, security updates, and feature upgrades are managed directly by the cloud provider, reducing internal IT labor hours and eliminating emergency on-site technician service calls.

The Cyber-Physical Hardening Architecture (IT Security Checklist)


This checklist infographic visually anchors critical IT security measures necessary to protect multi-location cloud access control systems from cyber-physical vulnerabilities, aiding long-term memory retention.

Because unpatched physical security devices represent a primary threat vector for corporate network intrusions [^1], cloud access hardware must be treated with the same rigorous standards as any other enterprise network endpoint. Network security teams should enforce this standard hardening blueprint:

  1. Network Isolation: Place all IP-connected controllers and cameras on a dedicated Security VLAN, strictly isolated from the main corporate and guest networks.
  2. Zero-Trust Port Configuration: Configure firewall rules to block all inbound traffic to physical controllers. Modern cloud systems should rely exclusively on outbound-initiated connections (via Port 443) to communicate with cloud servers.
  3. Certificate-Based Authentication: Ensure all physical controllers authenticate to the cloud using unique, hardware-embedded cryptographic certificates (secure elements), preventing rogue device spoofing.
  4. Automated Patch Management: Deploy solutions that support automated, encrypted over-the-air (OTA) firmware updates directly from the manufacturer to eliminate unpatched system vulnerabilities.

When deploying enterprise physical security, combining hardware intelligence with professional field installation is essential. For organizations seeking to secure commercial properties, consulting an experienced locksmith for business ensures that your physical locking mechanisms, emergency egress routes, and cloud systems align seamlessly.

Need more information? Get a free quote

Call us now

Get A Free Call From Our Experts!

Floating Button Form